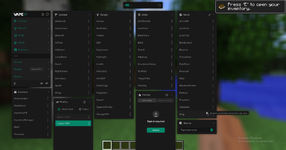
First of all Thank you to: @j0pek for providing me with this free.
I have no idea if the guy "Kangaroo" is credible or not, neither do i know if the version distributed under his name was made by him or not, innocent until proven guilty.
Anyways the sample I was provided with today, contains the "Divulge Stealer"
further info on that:
Findings:
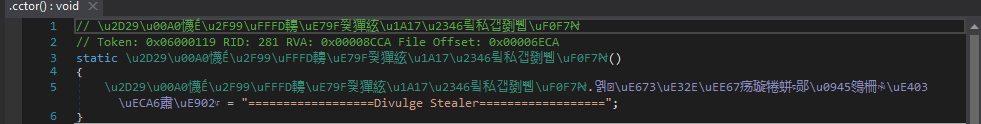
And other stuff, i am way to lazy to take screenshots of everything anyways the stealer will grab info from your device such as:
Discord Info such as Tokens and more,
Browser Sessions and Cookies,
Crypto Wallets,
Telegram Sessions,
and various System Information.
This information is all exfiltrated to:
Just dont be stupid and run it.
The effected file:
Vape V4.21.exe
SHA256: 0A0189197D9522E2E8C6BA806134BDD470C439912510E1B7DB35D1E773484948
QUICK EDIT: THE WEBHOOK IS DEAD AS WE SPEAK (404) SO THERE WILL BE NO EXFILTRATION ON THIS SPECIFIC BINARY; BUT THIS DOES NOT MEAN THAT RE-RELEASES OF IT UNDER A DIFFERENT HASH WITH A DIFFERENT WEBHOOK WILL BE SAFE.
I have no idea if the guy "Kangaroo" is credible or not, neither do i know if the version distributed under his name was made by him or not, innocent until proven guilty.
Anyways the sample I was provided with today, contains the "Divulge Stealer"
further info on that:
You must be registered for see links
Findings:
And other stuff, i am way to lazy to take screenshots of everything anyways the stealer will grab info from your device such as:
Discord Info such as Tokens and more,
Browser Sessions and Cookies,
Crypto Wallets,
Telegram Sessions,
and various System Information.
This information is all exfiltrated to:
You must be registered for see links
Just dont be stupid and run it.
The effected file:
Vape V4.21.exe
SHA256: 0A0189197D9522E2E8C6BA806134BDD470C439912510E1B7DB35D1E773484948
QUICK EDIT: THE WEBHOOK IS DEAD AS WE SPEAK (404) SO THERE WILL BE NO EXFILTRATION ON THIS SPECIFIC BINARY; BUT THIS DOES NOT MEAN THAT RE-RELEASES OF IT UNDER A DIFFERENT HASH WITH A DIFFERENT WEBHOOK WILL BE SAFE.
Last edited: