I used a lot of injectors but idk how to do a loadlibrary one..
When it comes to cheating, if we are dealing with an internal cheat, it usually comes as a .DLL file that needs to be injected. There are primary two methods that you have to know, LoadLibrary which is also called Standard injection and Manual Mapping (ManualMap).
LoadLibrary uses standard Windows API functions to inject the .DLL, meaning that operating system handles most of the work. In contrast, ManualMap, the injector performs everything itself. Thus it will manually resolve PE relocations, fix relative offsets, and repair the Import Address Table (IAT) so that the cheat’s dependencies function correctly.
Cheat developers often design their cheats to be injected in a specific way for certain reasons, such as bypassing anti-cheats. For example, when using ManualMap, the injected .DLL will not appear in the modules list because it is not registered in the PEB. However, with LoadLibrary, the .DLL is visible there. This distinction became particularly useful around 2020, when Valve introduced a new function that caused crashes for any .DLL injected into the game using LoadLibrary. As a result, it became necessary to use launch options like "-allow_third_party_software" or "-insecure" if you wanted to inject a cheat via LoadLibrary. ManualMap, however, can bypass this limitation.
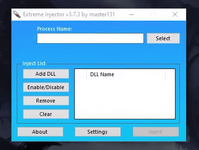
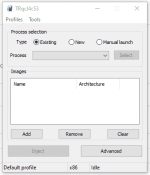
But when it comes to the core of your question, if you want to use both methods in the same injector, I would recommend Extreme DLL Injector or Xenos DLL Injector. Both of these injectors support these injection methods, along with several others that you don't have to know.
Extreme DLL injector:
Download Extreme Injector v3, a DLL injector for games with multiple options, simple use, a screenshot, and a VirusTotal link.

hackvshack.net
Xenos DLL injector:
Download Xenos 2.3.2 DLL Injector with native injection, manual map, kernel and delayed injection options, C++ source code, and a VirusTotal link.
hackvshack.net
In order to change method of injection in
Extreme DLL injector you have to go to "Settings", and then "Injection Method"

For
Xenos DLL injector you have to go to the "Advanced" and then you have "Injection type"

In conclusion Loadlibrary is default way of injecting .DLL file to the process which can be easily detected, while ManualMap injection is basically own native implementation of Loadlibrary, thus there is more flexibility, while this is important to mention that any of these methods won't bypass kernel anti-cheat, but from theoretical point of view if there is anti-cheat which is working in userland and it will scan all loaded modules only, ManualMap can bypass it.