BlackBox DLL Injector 1.0.2
High-Performance Pure Rust DLL Loader with In-Memory Manual Mapping & Crash Triage
BlackBox Injector is a modern, lightweight Windows DLL injector engineered entirely in pure Rust with zero third-party dependencies. Built directly on top of native Win32 and undocumented NTAPI syscalls, it offers rock-solid stability on modern Windows 11 and Windows 10 systems across both native x64 and 32-bit (WOW64) architectures.High-Performance Pure Rust DLL Loader with In-Memory Manual Mapping & Crash Triage
Supported Injection Methods
BlackBox gives you 6 different injection methods so you can always find the one that works best for your target:
- Method 0: Standard (CreateRemoteThread)
The classic, tried-and-true injection method. Simple, highly reliable, and works on almost all standard applications and DLLs. - Method 1: Native NT Loader (LdrLoadDll)
Calls the low-level Windows loader directly insidentdll.dll. It skips high-levelkernel32initialization, helping you bypass common user-mode API hooks. - Method 2: Manual Map (In-Memory PE Loader)
Loads your DLL directly into target memory without registering it in the Windows module list. Unlike older manual mappers that crash complex DLLs, BlackBox fully handles:- Full C++ exception support (
try/catchand SEH) so your DLL won't instantly crash when an exception is thrown. - Complete TLS support (both thread-local storage variables and TLS callbacks).
- Proper section memory protections and automatic import resolution.
- Full C++ exception support (
- Method 3: Thread Hijacking
Hijacks an existing, already-running thread inside the target process to load your DLL and immediately restores it. Creates zero new threads, avoiding detection from basic thread creation monitors. - Method 4: NtCreateThreadEx
Uses direct native system calls to spawn an injection thread while applying theThreadHideFromDebuggerflag to keep it hidden from attached debuggers. - Method 5: Threadless APC (QueueUserAPC)
Queues your DLL load onto an existing thread waiting in an alertable state. Completely threadless injection without spawning a single new thread.
Key Features & Compatibility
- Instant Crash Diagnostics & Error Reports
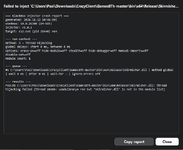
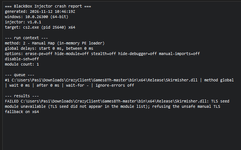
Tired of injectors closing silently or showing a useless "Injection Failed" error? If anything goes wrong or your game crashes, BlackBox immediately inspects the process, decodes the crash dump, and pops up a clear report telling you the exact reason (e.g. Access Violation0xC0000005, missing DLL, or bad forwarder) with a 1-click Copy Report button for easy troubleshooting. - Automatic VC++ Dependency Detection
Scans your DLL before injecting to check if you are missing required Visual C++ Redistributable runtimes (such asvcruntime140.dllormsvcp140.dll). Instead of letting your game crash silently, it tells you upfront exactly which runtime you need to install. - Windows 11 & Core Isolation Ready
Old injectors built years ago regularly crash on modern systems. BlackBox is written from scratch in pure Rust with zero third-party dependencies, running smoothly on Windows 10 and modern Windows 11 even with Core Isolation / Memory Integrity (HVCI) turned on. - Full 64-bit (x64) and 32-bit (x86) Support
Works seamlessly on both 64-bit and 32-bit (WOW64) applications. BlackBox automatically detects bitness mismatches so you never accidentally try to load a 32-bit DLL into a 64-bit process. - Built-In PE Cloaking & Scrambler
Includes optional stealth options right in the UI: erase PE headers from memory (ErasePE), unlink modules from the active PEB list (HideModule), and scramble binary signatures before loading.
Showcase
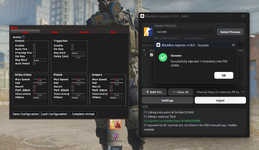
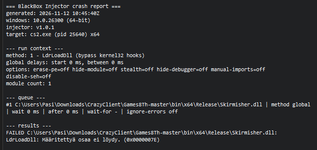
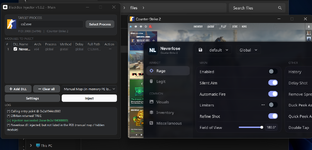
(Example: Injecting a 64-bit module (AyywareCS2.dll) into Counter-Strike 2 (cs2.exe) via Manual Map, successful injection YES MANUAL MAP IN BLACKBOX IS WORKING FOR CS2)
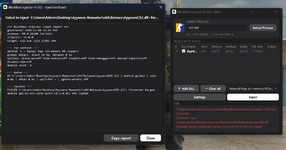
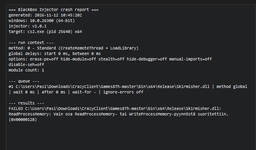
(Example: Injecting a 64-bit module (AyywareCS2.dll) into Counter-Strike 2 (cs2.exe) generates an automated failure report via Manual Map because an API-set forwarder dependency (api-ms-win-core-synch-l1-2-0.dll) is not loaded in the remote process.)
Thread Scope & Support
This thread serves as the official release and discussion hub for BlackBox Injector:
- Official Releases & Changelogs: All future version updates and latest pre-compiled standalone executables, will be posted directly here.
- Troubleshooting & Help: If an injection fails or a target exits unexpectedly, hit "Copy report" on the BlackBox diagnostic popup and paste it into a reply. The report pinpointing missing DLLs, dependency forwarders, or access violations makes troubleshooting instant.
- Feedback & Suggestions: Feel free to share feedback, feature requests, or compatibility reports with different DLL payloads.
Source Code & GitHub
What is covered on GitHub:
- Full Source Code: Inspect the complete pure Rust codebase, review native Win32/NTAPI implementations, or audit the memory loaders yourself.
- Issue Tracker & Reporting: Submit bug reports, request new features, or report compatibility issues with specific Windows builds.
You must be registered for see links
Changelog
1.0.2
- Changed: manual-map static TLS now registers the mapped image directly with LdrpHandleTlsData; the loader-visible seed DLL fallback was removed. The internal function is resolved from the matching ntdll PDB, cached in %TEMP%\BlackBoxInjector\symbols.
- Fixed: a target that is already gone, or a missing/undownloadable ntdll PDB, now uses the normal error dialog (E2003 TARGET_NOT_RUNNING / TLS-PDB-01) and no longer writes a failure report.
1.0.1
- Fixed: manual map static TLS now builds a real seed DLL sized exactly to the payload's TLS template. No fixed capacity, no unsafe manual thread-array fallback.
- Fixed: Standard and NtCreateThreadEx capture the 64-bit HMODULE through a remote stub and verify the PE at that base. DLLs that unlink themselves no longer produce a false "not in the module list" error.
- Fixed: crash reports map the WER exception code and fault offset correctly; the module timestamp is no longer shown as the exception code.
- Fixed: --cli ... > log.txt and pipes keep the caller's standard handles.
- Changed: one embedded TLS base seed instead of a size ladder; smaller binary and no 128 KB ceiling.
- Added: the TLS seed source (seed/tls_seed.cpp) and rebuild script (seed/build.cmd), so the prebuilt base DLL is reproducible and auditable.
1.0.0
- Initial release: six injection methods, manual map with TLS and C++ exception support, cloaking, crash diagnostics, CLI.
Password for .zip file is hvh.net
Last edited: