
Hello users!
People are getting rated by alot of LUAS that are infected with password stealers.
How to detect an infected LUA?
- The luas title is always the same like : AcidTech, Kenzo, Chimera, Maycray, Acatel, Elusive, Jag0yaw (cracks).
What to do if i see one of this LUAS?
- Report the thread.
Did you already executed this LUA before? what you should do :
- Verify your system (computer) with Anti-Virus + Windows Defender (I recommend using
- Change your passwords (URGENT)
thanks for relity because he makes this original post
EDIT:
Before using cheats (.lua), open it on notepad and search for "urlmon", check if there are any signs of "urlmon" downloading a .exe file, (mostly from cdn.discordapp.com), if you do find the said things, please report it to our team via in-site tickets or Discord tickets.
People are getting rated by alot of LUAS that are infected with password stealers.
How to detect an infected LUA?
- The luas title is always the same like : AcidTech, Kenzo, Chimera, Maycray, Acatel, Elusive, Jag0yaw (cracks).
- The download link is from discord like : https://
You must be registered for see links
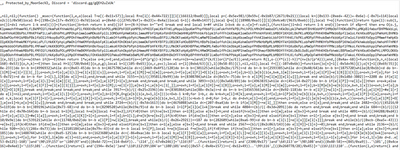
- The LUA is protected by MoonSec V2 (edit the LUA with notepad and you will see if its protected).
What to do if i see one of this LUAS?
- Report the thread.
- Reply the post saying that the LUA is a rat and say to not download the file.
- Of course DON'T execute this LUAS!
Did you already executed this LUA before? what you should do :
- Verify your system (computer) with Anti-Virus + Windows Defender (I recommend using
You must be registered for see links
)- Change your passwords (URGENT)
thanks for relity because he makes this original post
EDIT:
Before using cheats (.lua), open it on notepad and search for "urlmon", check if there are any signs of "urlmon" downloading a .exe file, (mostly from cdn.discordapp.com), if you do find the said things, please report it to our team via in-site tickets or Discord tickets.


