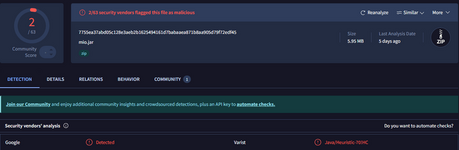
Analyze suspicious files to detect types of malware.
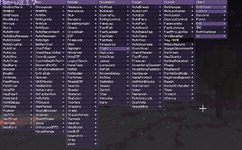
Screenshot of Cheat Menu:
Instructions to use here
You must be registered for see links
UPDATE: 2.2.1 free !
You must be registered for see links
EDIT - 2025/12/27
nick's github is down, i'll try my best to provide jars I had downloaded
to use the free, simply put both mods in the mods folder
1.21.1 for 2.1.7, 1.21.5 for 2.2.1
source of the free is also public, you can read all the code to know it's safe
here's a crystalpvp.cc all preset config
This mod has a backdoor. Just a few days after I tried using it, my Google account and associated Steam and Discord accounts were stolen. I'm certain this all happened because I only used this mod.
This mod has a backdoor. Just a few days after I tried using it, my Google account and associated Steam and Discord accounts were stolen. I'm certain this all happened because I only used this mod.
What is casual link between this situation and this mc client? Since your statement is not backed by concrete evidence, but rather intuition, thus it is hard to take it serious.
What is casual link between this situation and this mc client? Since your statement is not backed by concrete evidence, but rather intuition, thus it is hard to take it serious.
its not ratted plisskien cuz if it was my steam with 11k elo and skins would be already taken same with my discord and other shit plus its hard to believe that Twonick would backdoor it
This mod has a backdoor. Just a few days after I tried using it, my Google account and associated Steam and Discord accounts were stolen. I'm certain this all happened because I only used this mod.
"This mod has a backdoor" and you do not proceed to give any evidence for this statement, the loader for both versions is fully un-obfuscated which you could analyze yourself using JDGui or Recaf, for the 2 Mio Jar files itself those have "heavy" obfuscation applied to them but that was likely already done by the original author of the client, still static analysis is possible for JVM Bytecode which would give you yourself the option to check them and and gather proof for your claims, yet you decide to give us a nothing burger backed up by empty claims about your accounts being stolen.
This mod has a backdoor. Just a few days after I tried using it, my Google account and associated Steam and Discord accounts were stolen. I'm certain this all happened because I only used this mod.
This site uses cookies to help personalise content, tailor your experience and to keep you logged in if you register.
By continuing to use this site, you are consenting to our use of cookies.