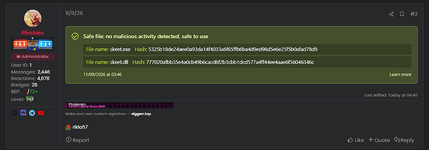
If the source free on the russian pasting forum is correct, this DLL
could be malicious.
Source can be found on russian pasting forum here:
You must be registered for see links
I would advise to not run the DLL before analyzing the entire source.
It looks for connectivity and wants to pass a
payload.
Source is based of Nexoria [Velocity Paste]
There is a certain
python file found within the source that can do the following:
- Start/stop/status APIs
- worker-thread management
- WinHTTP authentication
- UDP/TCP Connection to and a specific server:
nexoriamods.com
- validation of a launch ticket
- process identity using GetProcessTimes
- wiping secrets from memory
- cancellation of HTTP requests
- thread-pool shutdown
- Control Flow Guard and buffer-security compiler settings
- behavior when the DLL cannot safely be unloaded
->
You must be registered for see links
checks code involving a
target PID,
target creation time, and
payload SHA-256.
Take what i said here with a grain of salt, i could be wrong.
Hopefully the forum staff analyzes this for us.