Welcome to hackvshack.net Forum!
Download Free HvH CS2/CS:GO Cheats, CFG, LUA/JS Scripts, and More!
Register

Safe TFGhost DLL Injector + VAC Bypass for Team Fortress 2

Plisskien

Administrator
User ID:
1
Messages:
2,395
Reactions:
4,652
Badges:
28
REP:
−2/64+
Level:
740
VirusTotal.com Link:
Analyze suspicious files to detect types of malware.

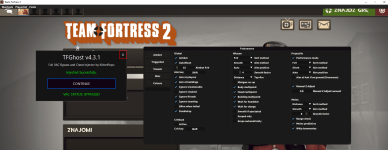
SS of this DLL injector + Bypass:
c05cf55166a6e5b7ad638b6861ce1eac.png

So th
is is just CSGhost v4.3.1, made by KittenPopo. It was edited by me (@Plisskien) via Hex edit to work on game TF2.
I was testing it few times, everything was working, if you have any problems, write below!

Orginal Source:
 

Password for .zip file is hvh.net

does'n work, bitch! it says error! :(
THIS IS CHEATS ALL OUTDATED ARE NO MORE!!!! PROB GABEN NEWELL BLOCKED ALL CHEATS FROM TEAM FORTRESS 2!
 
when the vac is by passed and when the time for come to load the dll the button does not pope out
help me please i need answer to know if any one got the same probem as me
Thanks.
 
just btw its clearly a goshing virus i mean like
According to you? That's great, I would like to point out that this is DLL injector, thus it will inject DLL to process, and there is also included VAC bypass that will block this module, thus the same structure could be theoretically used to bypass antivirus, and run malicious code. What I'm referring to is fact that same logic was used in past for malicious purposes, and similar signature is being detected by these anti-malware engines. Also I would like to point out that these detections engines are not normal detection engines rather they are oversensitive in order not to skip any threat, something like this would be very annoying on normal PC. To sum up virustotal is great solution for checking files, but at the same time looking at detections for this type of file is showing lack of knowledge... If you see cheat file with many detections like TROJAN etc... this is good sign, because most cheats use old good methods that were used in past for malwares. Thus if you see file that is cheat file and it is PE, with very small amount of detections and this is C++ cheat we can assume that such file might be malicious, and this is not a cheat, rather dropper or crypter, with surprise under the hood.
 
VirusTotal.com Link:
Analyze suspicious files to detect types of malware.

SS of this DLL injector + Bypass:
c05cf55166a6e5b7ad638b6861ce1eac.png

So th
is is just CSGhost v4.3.1, made by KittenPopo. It was edited by me (@Plisskien) via Hex edit to work on game TF2.
I was testing it few times, everything was working, if you have any problems, write below!

Orginal Source:
uhhh, it's stuck on "waiting for tf2..." how do i fix this?
 
this is tfghost x32 bit doesn't working normal where before they update team fortress 2 but update x64 plus bit tfghost cannot waiting system he just stuck here forever you can ask creator like Plisskien to answer him he will made update or not but the while we just gonig wait here is no one know answer what will to more make it's lookling like oh but the way i didn't test FUFUGUA from github if so try use if you want is that all
 
Oh my god u spastic, I said this THREAD is 3 years old. I did NOT say U were
oh i am sorry my bad actually i am delete him Because is take me long time and sorry again i thought you talk to me and yeah thanks for you tell me is old and now I Focusing who is hack made and bye have great time
 

Who has read this thread (Total: 0) in last 1 hours View details