Welcome to hackvshack.net Forum!
Download Free HvH CS2/CS:GO Cheats, CFG, LUA/JS Scripts, and More!
Register

Info Gamesense free Malware

i did try it and fact the resolver is "good", esp is like in real gs but my system sometimes freezes in random situations but thats my computer problem and not cuz of cheat so
 
In the end of the day you gotta always take a risk when using a cheat

I run every damm loader and dll from multiple servers and yougame ( which should be the best choice ) and like there are strings for like some api for pushover but like in 2 hours using it no traffic at all to anything meaning the allegations are probaly some bs and the guy is trolling so nobody uses skeet


might be still infected just use a damm VM ( hyper v windows with gpu passthrough best choice ) see on yt how that would be the easiest thing to do to cheat with it and not get infected if it is
 
I approved this file as unknown. While it seems safe, I'm not 100% certain
https://hackvshack.net/threads/gamesense-free-by-expandera.5690/

For testing, I installed a fresh Windows system on physical machine where I proxied all traffic. I monitored it for about 15 minutes after injection and detected no suspicious activity. I also tested it after a system restart, and still found nothing suspicious. I monitored it with a spoofed process monitor as well, and there were no signs of malicious behavior. Based on this testing, I believe the file is likely safe. Even if we look at static analysis there are a few red flags, but we have to take into account that this is a free cheat, thus some suspicious indicators are expected, thus the best idea is just to run it, and I couldn't find anything... I would like to also indicate that my way of testing it was probably the most stealthy way, since it wasn't a virtual machine, and at the same time I was proxying all traffic through another computer. Thus, my sandbox was lacking any easily detectable factors, that could be used to not execute payload.

Additionally, this pastebin link (pastebin.com/raw/nTYLedRK) It makes no sense, and the Discord screenshots don't explain anything. It was just clickbait to get people to join their Discord server... pathetic.
 
I approved this file as unknown. While it seems safe, I'm not 100% certain
https://hackvshack.net/threads/gamesense-free-by-expandera.5690/

For testing, I installed a fresh Windows system on physical machine where I proxied all traffic. I monitored it for about 15 minutes after injection and detected no suspicious activity. I also tested it after a system restart, and still found nothing suspicious. I monitored it with a spoofed process monitor as well, and there were no signs of malicious behavior. Based on this testing, I believe the file is likely safe. Even if we look at static analysis there are a few red flags, but we have to take into account that this is a free cheat, thus some suspicious indicators are expected, thus the best idea is just to run it, and I couldn't find anything... I would like to also indicate that my way of testing it was probably the most stealthy way, since it wasn't a virtual machine, and at the same time I was proxying all traffic through another computer. Thus, my sandbox was lacking any easily detectable factors, that could be used to not execute payload.

Additionally, this pastebin link (pastebin.com/raw/nTYLedRK) It makes no sense, and the Discord screenshots don't explain anything. It was just clickbait to get people to join their Discord server... pathetic.
Its always the same shit

they always claim everything is a rat the moment something gets free and pull up "evidence" that makes no sense with no dynamic analysis proof
 
I approved this file as unknown. While it seems safe, I'm not 100% certain
https://hackvshack.net/threads/gamesense-free-by-expandera.5690/

For testing, I installed a fresh Windows system on physical machine where I proxied all traffic. I monitored it for about 15 minutes after injection and detected no suspicious activity. I also tested it after a system restart, and still found nothing suspicious. I monitored it with a spoofed process monitor as well, and there were no signs of malicious behavior. Based on this testing, I believe the file is likely safe. Even if we look at static analysis there are a few red flags, but we have to take into account that this is a free cheat, thus some suspicious indicators are expected, thus the best idea is just to run it, and I couldn't find anything... I would like to also indicate that my way of testing it was probably the most stealthy way, since it wasn't a virtual machine, and at the same time I was proxying all traffic through another computer. Thus, my sandbox was lacking any easily detectable factors, that could be used to not execute payload.

Additionally, this pastebin link (pastebin.com/raw/nTYLedRK) It makes no sense, and the Discord screenshots don't explain anything. It was just clickbait to get people to join their Discord server... pathetic.
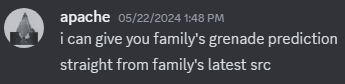
so you are telling me that this is safe... am i trippin or sum
 

Who has read this thread (Total: 0) in last 1 hours View details