Welcome to hackvshack.net Forum!
Download Free HvH CS2/CS:GO Cheats, CFG, LUA/JS Scripts, and More!
Register

Safe Net CS2 LIGHTMOON best external cheat Legit/semi-rage Auto update!

Status
Thread closed. Topic resolved/outdated. For updates, start new thread. Files removed to save server space.
I did a static analysis of this file in Ghidra because I was concerned about the VirusTotal detections.


Here is what I found:


The program uses InternetOpenUrlA to download files from GitHub (raw.githubusercontent).


It downloads files like offsets.hpp, client_dll.hpp, and FAQ.md.


It uses WriteFile, but through standard C++ runtime functions (likely for config/offset saving).


It calls CreateProcessAsUserA, but the command line passed is simply the result of GetCommandLineA().
This means it relaunches itself with the same command line (likely for privilege/token adjustment).


There are no signs of injection APIs, such as:


  • VirtualAllocEx
  • WriteProcessMemory
  • CreateRemoteThread
  • NtCreateThreadEx

There are no suspicious command executions like:


  • cmd.exe
  • powershell
  • rundll32

No obvious credential-stealing or browser-access APIs.


No secondary executable being dropped and executed.


The presence of OpenProcess alone does not indicate malware. It can be used simply to check if the game process is running.


Based on the analysis, the behavior matches a typical external cheat loader with an online offset updater.


VirusTotal detections are mostly generic / ML-based (GameHack / PUA classifications), which is expected for cheat software.


From a technical standpoint, I did not find evidence of this being a trojan, dropper, RAT, or stealer.


Risk Assessment (Based on My Analysis)​


  • 85% → Cheat / GameHack
  • 10% → Poorly written loader
  • 5% → Hidden trojan (no evidence found)


Disclaimer​


If there is any malicious behavior or hidden payload that I failed to detect during my analysis, I do not accept responsibility. Any decision to run this file is entirely at your own risk.
 
  • Jesus
Reactions: Plisskien
I did a static analysis of this file in Ghidra because I was concerned about the VirusTotal detections.


Here is what I found:


The program uses InternetOpenUrlA to download files from GitHub (raw.githubusercontent).


It downloads files like offsets.hpp, client_dll.hpp, and FAQ.md.


It uses WriteFile, but through standard C++ runtime functions (likely for config/offset saving).


It calls CreateProcessAsUserA, but the command line passed is simply the result of GetCommandLineA().
This means it relaunches itself with the same command line (likely for privilege/token adjustment).


There are no signs of injection APIs, such as:


  • VirtualAllocEx
  • WriteProcessMemory
  • CreateRemoteThread
  • NtCreateThreadEx

There are no suspicious command executions like:


  • cmd.exe
  • powershell
  • rundll32

No obvious credential-stealing or browser-access APIs.


No secondary executable being dropped and executed.


The presence of OpenProcess alone does not indicate malware. It can be used simply to check if the game process is running.


Based on the analysis, the behavior matches a typical external cheat loader with an online offset updater.


VirusTotal detections are mostly generic / ML-based (GameHack / PUA classifications), which is expected for cheat software.


From a technical standpoint, I did not find evidence of this being a trojan, dropper, RAT, or stealer.


Risk Assessment (Based on My Analysis)​


  • 85% → Cheat / GameHack
  • 10% → Poorly written loader
  • 5% → Hidden trojan (no evidence found)


Disclaimer​


If there is any malicious behavior or hidden payload that I failed to detect during my analysis, I do not accept responsibility. Any decision to run this file is entirely at your own risk.
dude who are you??? lol, you're going around on APPROVED cheats yapping about analysis, if you want to be a file analyzer then i'm sure this is not the way xD
 

User is currently banned.

I did a static analysis of this file in Ghidra because I was concerned about the VirusTotal detections.


Here is what I found:


The program uses InternetOpenUrlA to download files from GitHub (raw.githubusercontent).


It downloads files like offsets.hpp, client_dll.hpp, and FAQ.md.


It uses WriteFile, but through standard C++ runtime functions (likely for config/offset saving).


It calls CreateProcessAsUserA, but the command line passed is simply the result of GetCommandLineA().
This means it relaunches itself with the same command line (likely for privilege/token adjustment).


There are no signs of injection APIs, such as:


  • VirtualAllocEx
  • WriteProcessMemory
  • CreateRemoteThread
  • NtCreateThreadEx

There are no suspicious command executions like:


  • cmd.exe
  • powershell
  • rundll32

No obvious credential-stealing or browser-access APIs.


No secondary executable being dropped and executed.


The presence of OpenProcess alone does not indicate malware. It can be used simply to check if the game process is running.


Based on the analysis, the behavior matches a typical external cheat loader with an online offset updater.


VirusTotal detections are mostly generic / ML-based (GameHack / PUA classifications), which is expected for cheat software.


From a technical standpoint, I did not find evidence of this being a trojan, dropper, RAT, or stealer.


Risk Assessment (Based on My Analysis)​


  • 85% → Cheat / GameHack
  • 10% → Poorly written loader
  • 5% → Hidden trojan (no evidence found)


Disclaimer​


If there is any malicious behavior or hidden payload that I failed to detect during my analysis, I do not accept responsibility. Any decision to run this file is entirely at your own risk.
Chatgpt AHHHHHHHHH reply
studio bighead GIF
 
Menu key : İnsert/ins

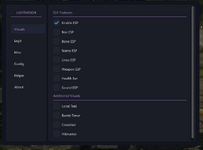
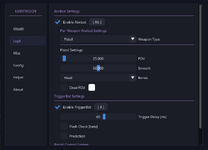
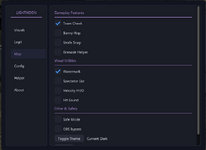
Screenshot of Menu/ESP/Aim/Misc
スクリーンショット 2025-09-26 120539.png
スクリーンショット 2025-09-26 120604.png
スクリーンショット 2025-09-26 120615.png

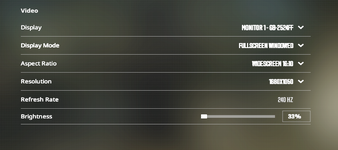
Recommended resolution settings
スクリーンショット 2025-09-26 121106.png

This is the recommended resolution. If you use it at this resolution, you won’t experience ESP shifting, ESP not appearing on the screen, or other weird issues.

------------------------------
Setup
Well, how do you install it? If I had to explain that too, here’s what I’d say xd Take the file you were given, extract it from the zip, open CS2, and while in the lobby run the exe. Within about 3 seconds, you’ll see the menu. Have fun.
-----

Config/Scripts Location:
I don't know
insert key not opening menu in game? i can see the text top left of screen showing fps and name but the cheat menu will just not open when inserting, i have tested if my insert key works and it is functioning properly. even used on screen keyboard to test.
 
Status
Thread closed. Topic resolved/outdated. For updates, start new thread. Files removed to save server space.

Who has read this thread (Total: 0) in last 1 hours View details